✓ Why they passed vetting
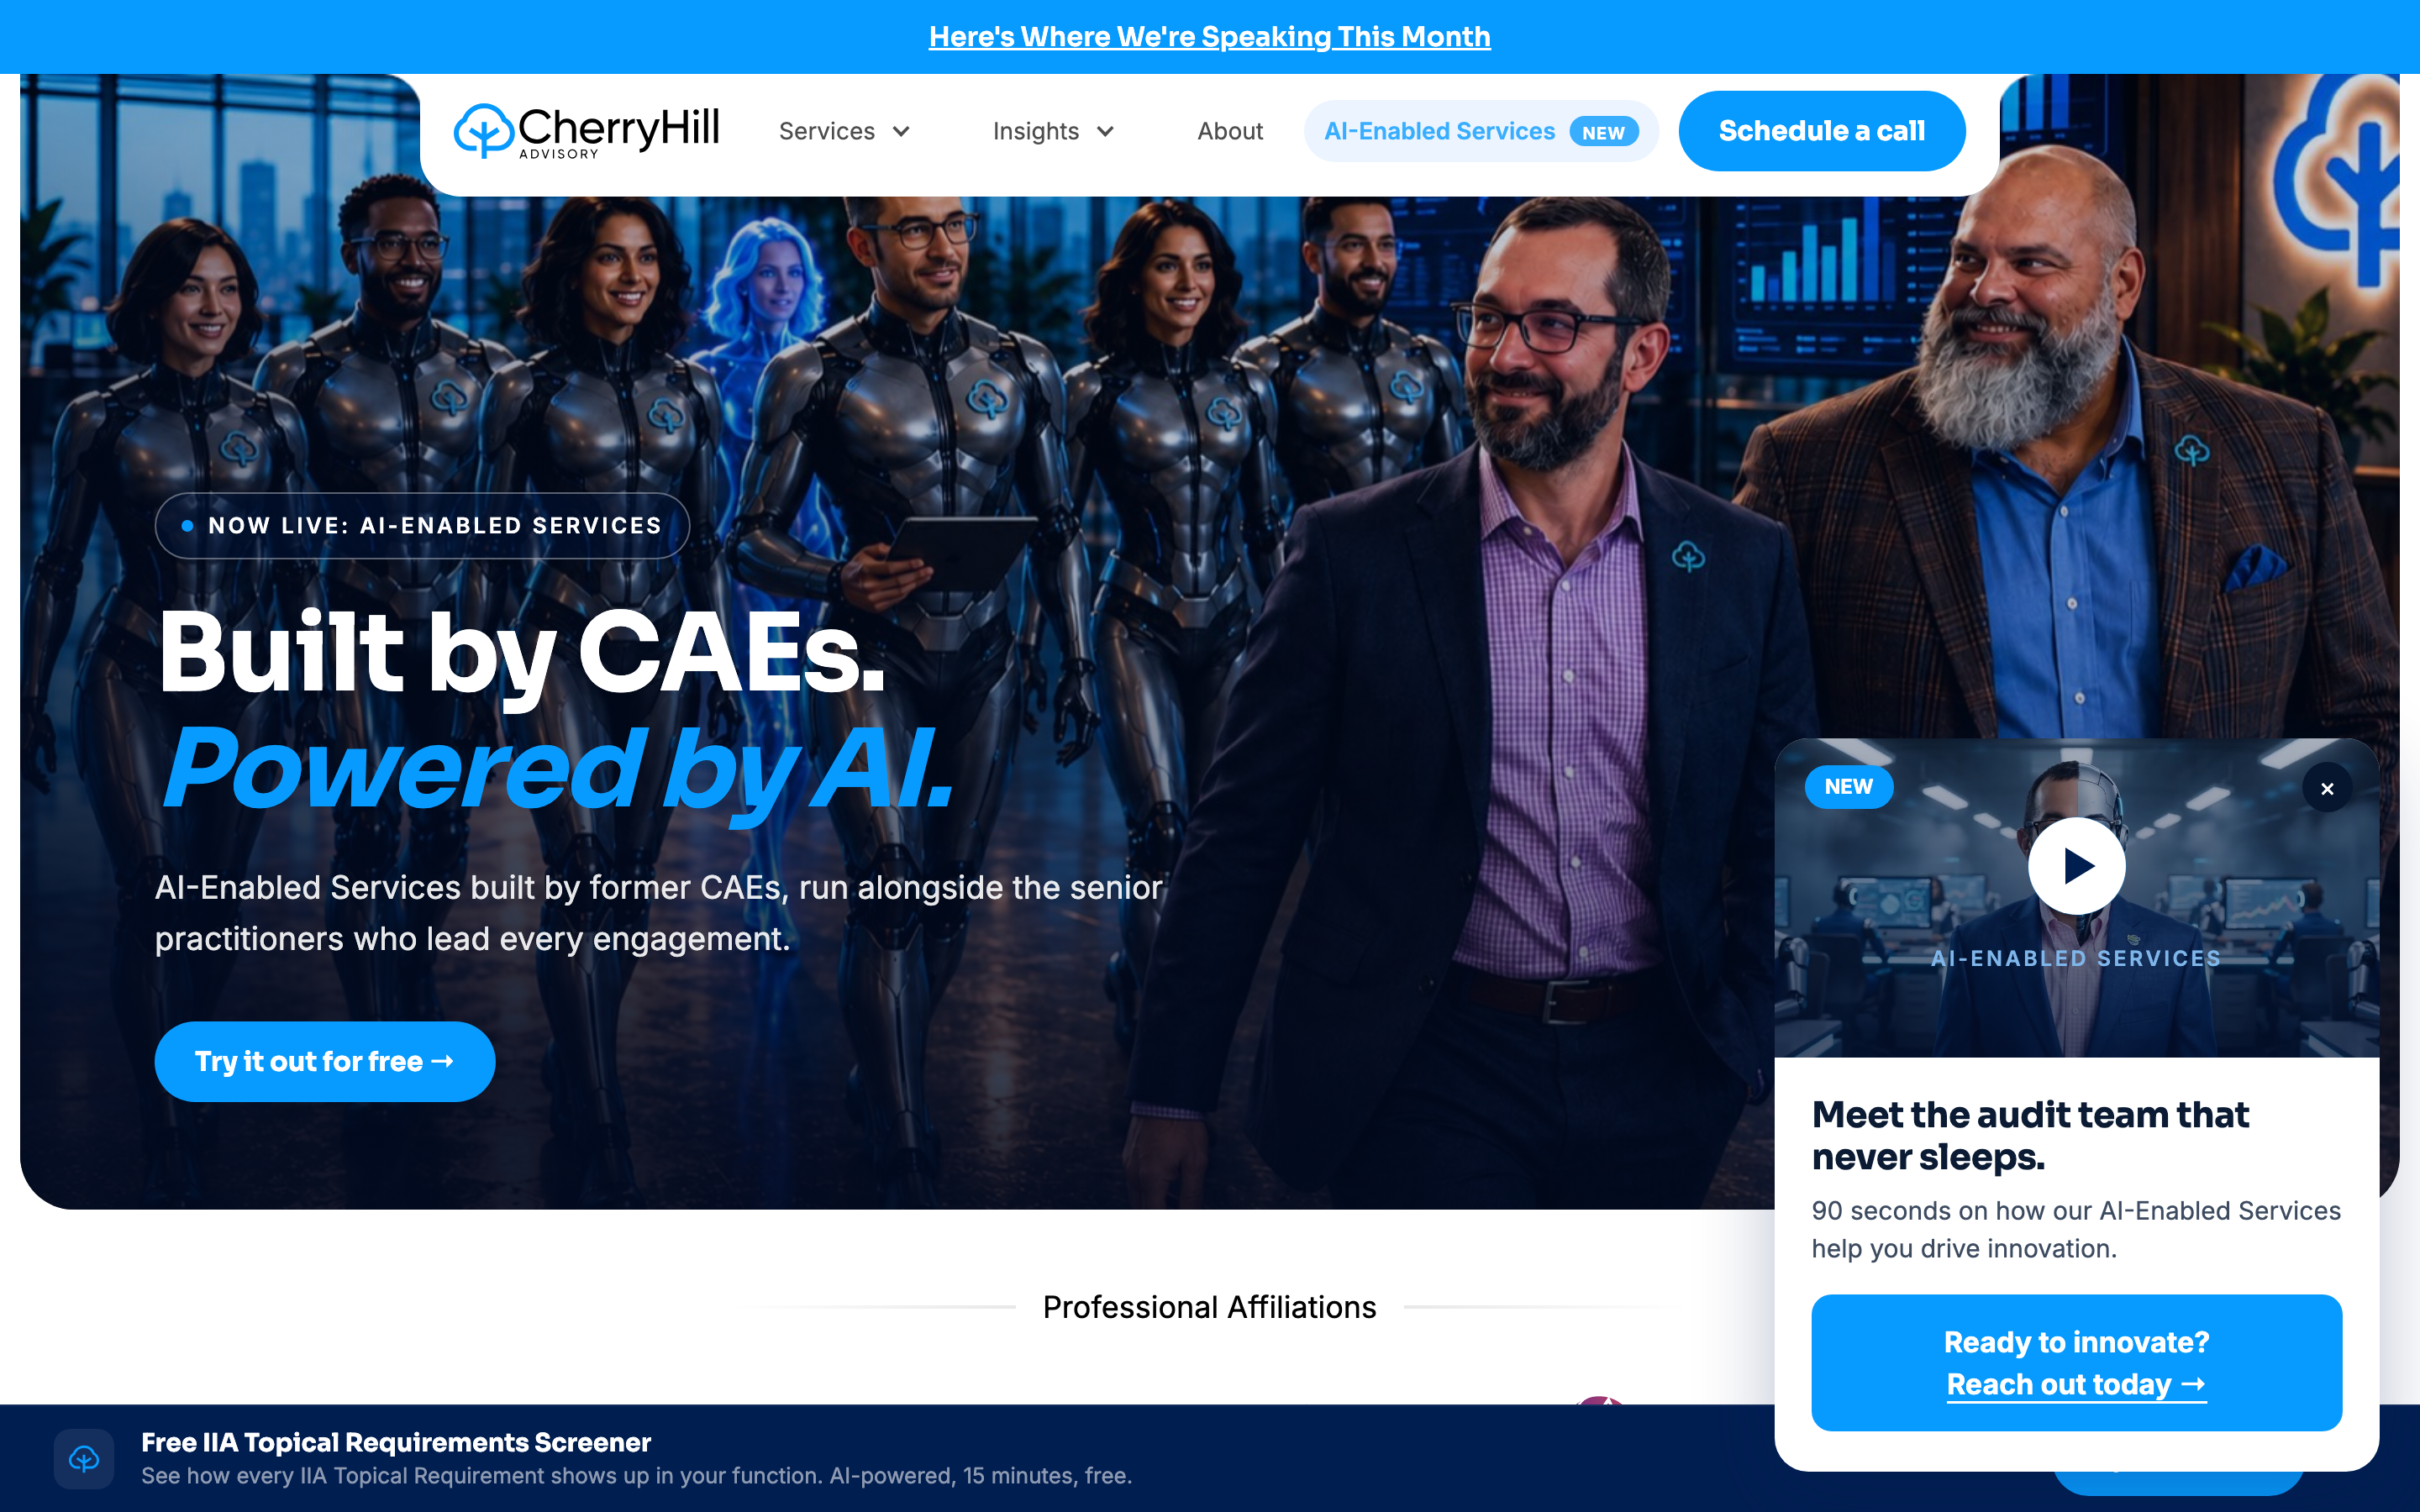
The service list is the whole of a modern internal audit remit rather than a slice of it: co-sourcing, external quality assessments against IIA Standards, SOX compliance and advisory, fraud risk and investigations, AI governance, cybersecurity and technology risk, and IT and cybersecurity expert witness work. Senior-led and accountable. You deal with people who have run audit functions, not a junior team working from a template, which is the usual complaint about the big firms. They are ahead on the risks that are hardest to hire for. AI governance and emerging risk are a named service here, not a slide. They publish training, events and internal audit readiness tools, plus regular thought leadership on things like where SOX programmes waste effort. Useful whether or not you engage them.